Skip to content
MC
/// Software engineering + application security

Secure software.
Engineered to endure.

I design and build production-grade digital products where sharp engineering and application security work as one discipline.

Built across the full delivery surface

Next.jsTypeScriptSupabaseAppSecOWASP

01 /// PROFILE

About

Mohamad Chalhoub is a Beirut-based software engineer and security specialist, building full-stack products since 2017.

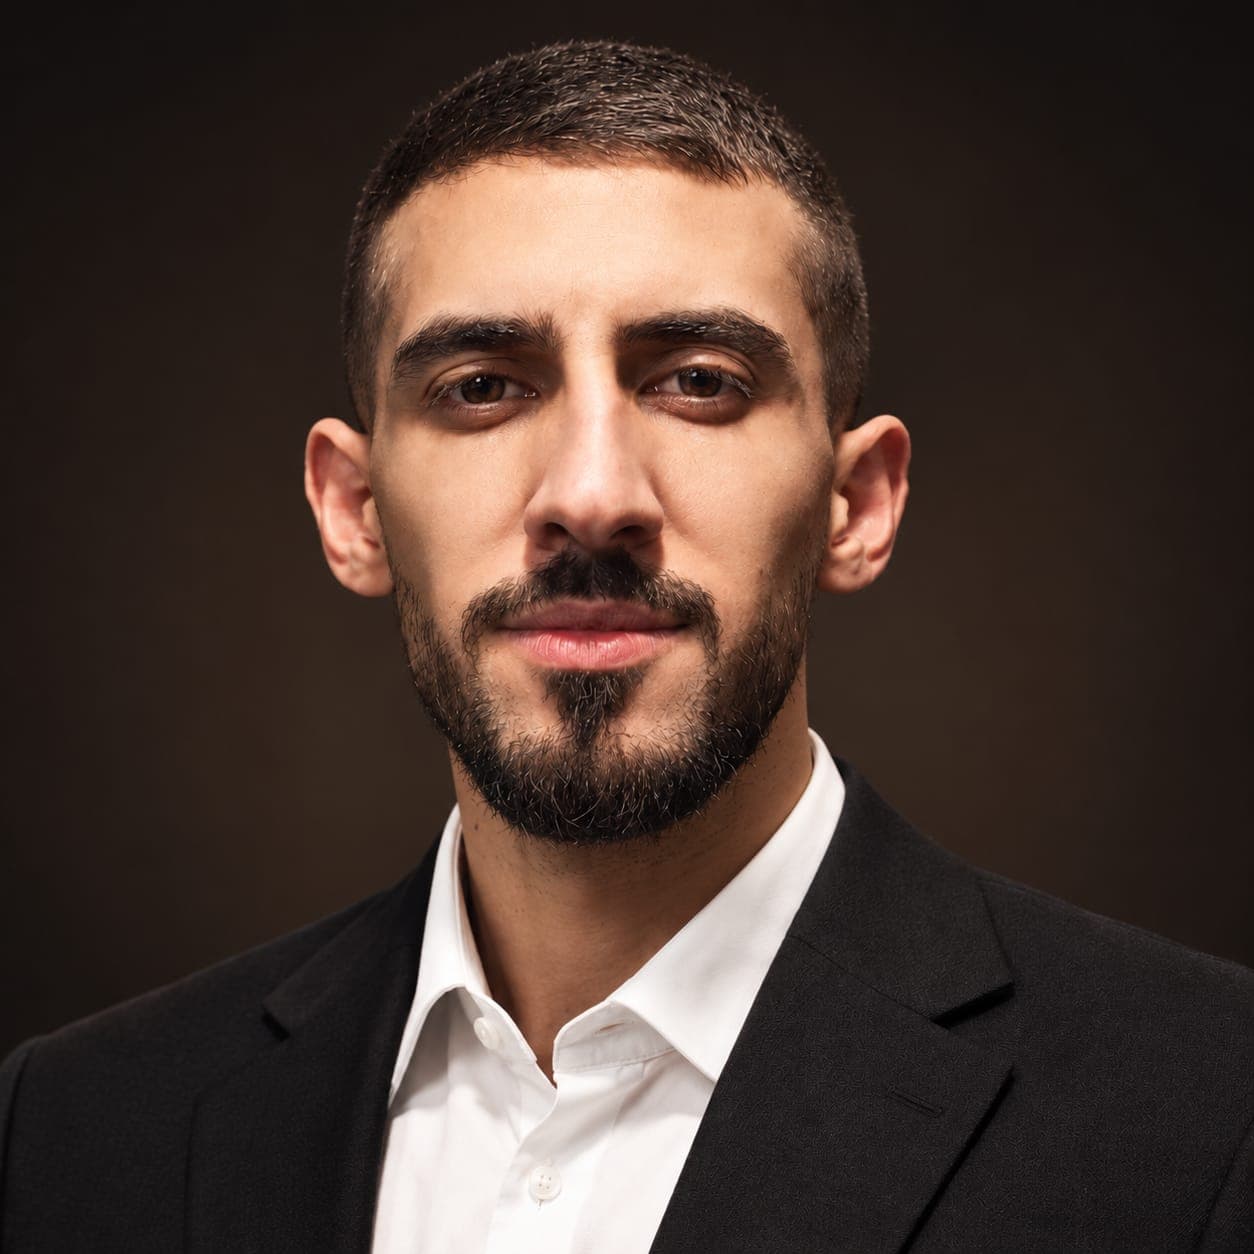
Portrait of Mohamad Chalhoub
Based in
Beirut, Lebanon
Active since
2017
Languages
Arabic (native) · English · French (B2)

2017

Building products since

04

Shipped case studies

02

Engineering disciplines

03

Working languages

02 /// CAPABILITIES

What I bring to a build

Two disciplines, applied together rather than handed off between specialists.

01

SVC // engineering

Software Engineering

Full-stack applications that stay maintainable as they grow, from the database up to the interface.

  • +Full-stack web applications
  • +Frontend architecture
  • +Backend systems and APIs
  • +Database design
  • +Authentication and authorization
  • +Performance and maintainability
02

SVC // security

Application Security

Applications assessed and built the way an attacker would look at them, before they ship — not after.

  • +Web application testing
  • +API security assessment
  • +Authentication and session testing
  • +Authorization and access-control review
  • +Reconnaissance and attack-surface analysis
  • +Security-conscious development

03 /// STACK

Technical Toolbox

Grouped by domain, not stacked as a wall of logos.

Cybersecurity

  • Web and API penetration testing
  • Reconnaissance
  • Attack-surface analysis
  • Authentication and session assessment
  • Authorization testing
  • Input-validation testing
  • Common OWASP vulnerability classes
  • Security reporting and remediation guidance
  • Secure application architecture

Software Engineering & Development

  • React & Next.js
  • Node.js & Express
  • TypeScript / JavaScript
  • MySQL & MongoDB
  • Java & Android (native)
  • Three.js / React Three Fiber

04 /// SELECTED_WORK

Evidence of how I think,
and what I have shipped.

Selected client projects, plus anonymized security findings presented without exposing private platforms.

Responsible disclosure experience

Anonymized security findings

I include bug classes and remediation thinking only at a high level. Platform names, private reports, proofs of concept and client-sensitive details stay confidential.

Real experience, integrity-first presentation

Authorization

Access-control and object-level permission issues

Session security

Login, token and session lifecycle weaknesses

Input handling

Validation issues that can expose unsafe behavior

Configuration

Headers, policy and deployment hardening gaps

Selected client delivery

Products built end-to-end

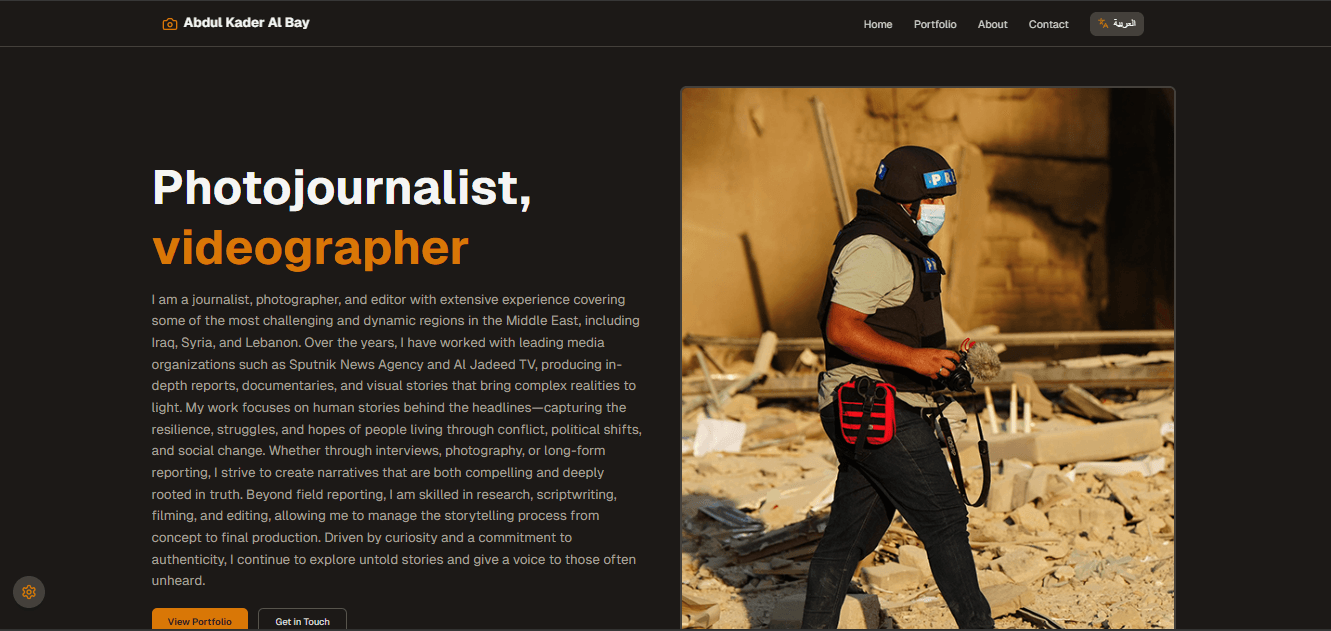
Abdul Kader Al Bay photography portfolio homepage
Case study 01 Shipped

Abdul Kader Al Bay

Photography portfolio with a bilingual content workflow

A Next.js site backed by Supabase, with an admin dashboard for managing galleries and content directly, and multi-language support built into the routing and data model rather than bolted on.

  • Admin dashboard for publishing and organizing galleries
  • Supabase-backed content and media storage
  • Multi-language content delivery
  • Next.js
  • Supabase
  • TypeScript
  • Tailwind CSS
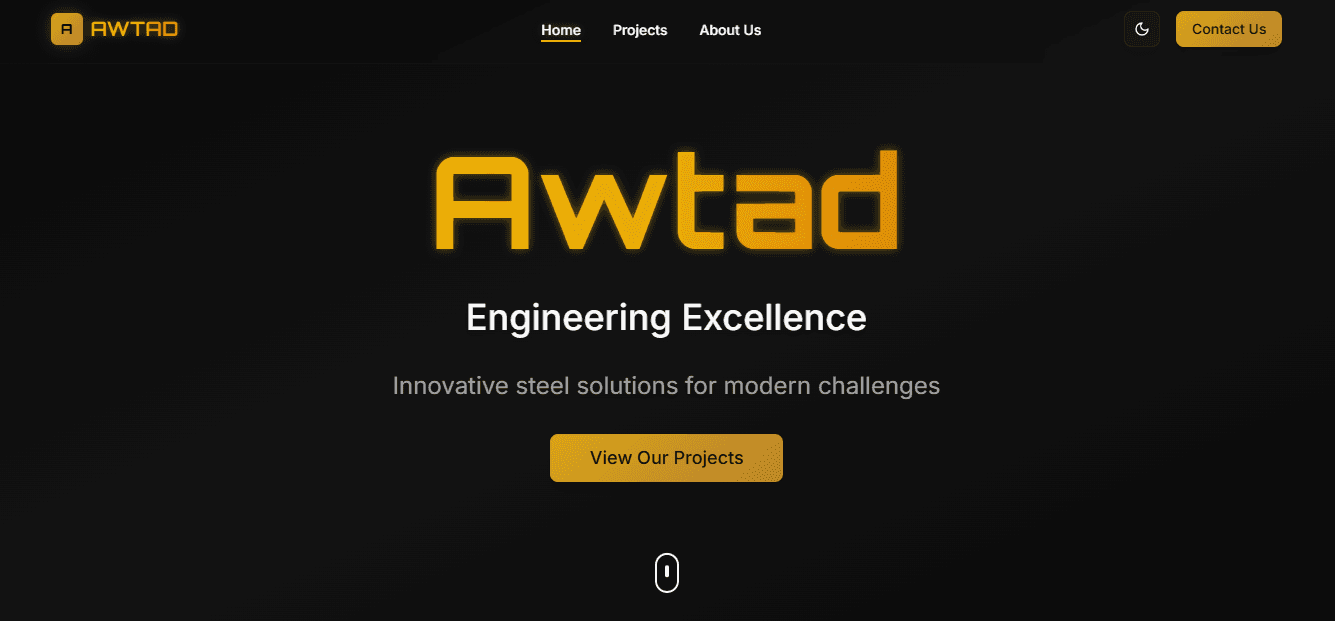
AWTAD steel design and engineering website homepage
Case study 02 Shipped

AWTAD

Steel design & engineering company website

A responsive Next.js and Supabase site presenting the firm's services and engineering focus with a clean, content-led layout built for clarity over decoration.

  • Structured service and capability pages
  • Supabase-backed content so copy can be updated without a redeploy
  • Responsive layout tested across desktop and mobile breakpoints
  • Next.js
  • Supabase
  • Responsive design
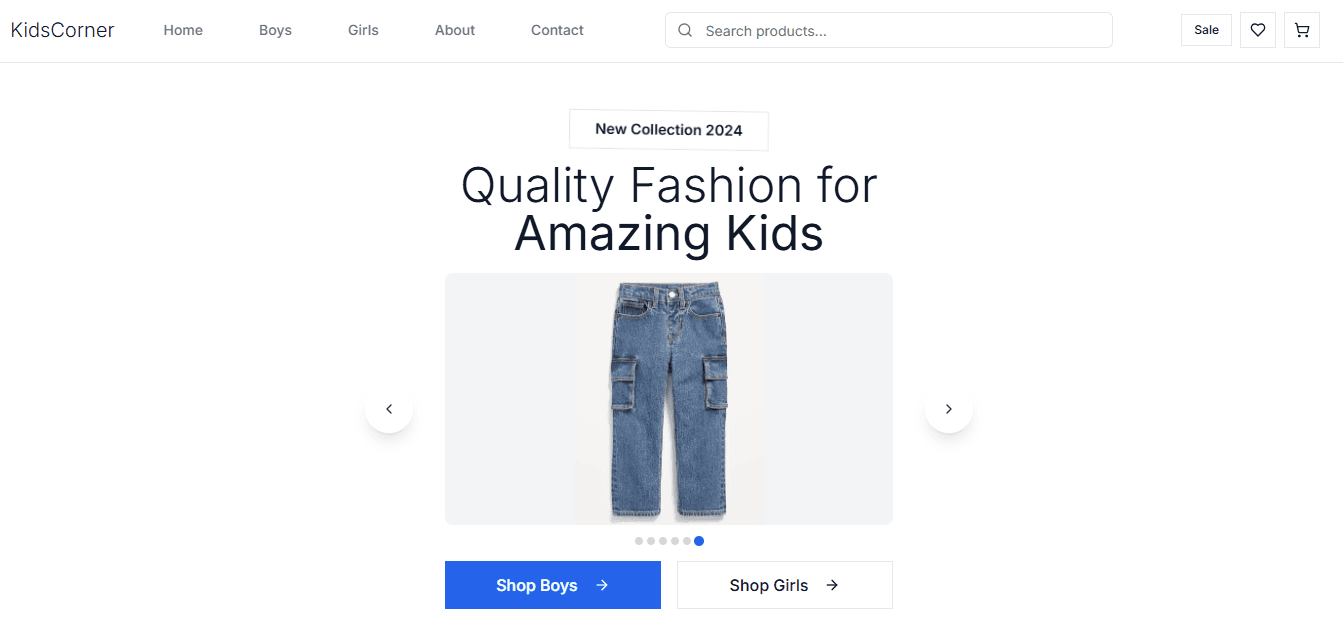
KidsCorner children's fashion e-commerce homepage
Case study 03 Shipped

KidsCorner

Children's fashion e-commerce platform

A full-stack e-commerce platform built with Next.js, TypeScript and Supabase, pairing a customer-facing storefront with an administration dashboard for day-to-day operations.

  • Product catalog with cart and checkout flow
  • User authentication for customer accounts
  • Payment processing integration
  • Next.js
  • TypeScript
  • Supabase
  • Tailwind CSS

05 /// APPLICATION_SECURITY

Security is part of the architecture.

Alongside client work, I conduct independent security research and participate in bug-bounty programs on public disclosure platforms, following responsible-disclosure practices: findings go to the affected organization first, on their terms, before anything is made public.

Specific findings and the organizations involved stay confidential, in line with responsible disclosure. What's demonstrable is the methodology: systematic reconnaissance, structured testing against authentication, authorization and input handling, and remediation guidance written for the team that has to act on it.

Assessment coverage

Application surface · structured methodology

Responsible disclosure

Method

01Map the attack surface
02Test trust boundaries
03Report actionable fixes
  • Web and API penetration testing
  • Reconnaissance
  • Attack-surface analysis
  • Authentication and session assessment
  • Authorization testing
  • Input-validation testing
  • Common OWASP vulnerability classes
  • Security reporting and remediation guidance
  • Secure application architecture

06 /// DELIVERY_PROTOCOL

Working Method

Engineering, design and security are handled together at every stage, not treated as separate hand-offs.

01Understand

Start with the problem, not the tech. Clarify what the product needs to do, who it serves, and what 'done' actually looks like.

02Architect

Design the data model, the API surface, and the trust boundaries together — authentication and authorization are decided at this stage, not bolted on later.

03Build

Implement in typed, componentized code with content and presentation kept apart, so the product stays easy to extend after launch.

04Test

Verify behavior across devices and edge cases, not just the happy path — including how the interface degrades without JavaScript or WebGL.

05Secure

Review the same application from an attacker's perspective: input handling, session management, access control, and the server-side validation that backs every client-side check.

06Deliver

Ship something that performs, reads clearly, and holds up — with the reasoning behind each decision documented, not just the code.

07 /// SECURE_CHANNEL

Let’s build something
clients trust.

Tell me what you’re building. I’ll reply personally to discuss scope, timeline and fit.

Available for selected projects
Private contactUse the secure form
LinkedInConnect
Send a message
I typically reply within a couple of days.